Suspected Security Incident Report Form Template
Make it easier to describe a digital security concern without requiring a technical diagnosis. Adapt these seven initial report fields and your organization's real reporting instructions in SurveyLegend.
Make it easier to describe a digital security concern without requiring a technical diagnosis. Adapt these seven initial report fields and your organization's real reporting instructions in SurveyLegend.
A suspicious message does not automatically mean a breach occurred. A reporter should be able to explain what they saw and which service was involved while the designated security team determines the next step.
When to Use This Template
Use this as an initial notification only after your security team approves the collection channel, access controls, and monitoring process. For ordinary product questions without a security concern, use a separate support request form . An active urgent incident must follow the organization's established escalation route.
7 Suspected Security Incident Report Form Questions
Report one suspected digital security concern using general descriptions. You do not need to confirm a breach. Do not include passwords, access codes, customer data, full message contents, suspicious clickable links or files. Every field is optional. Use the organization's stated urgent reporting route if immediate attention is needed; this form alone does not guarantee a response.
A little feedback. A clearer picture.
Explore this 7-question example at your own pace. Every question is optional.
Suspected Security Incident Report Form
Thank you for trying the survey!
You’ve tried the template from the respondent’s side. Make it your own with SurveyLegend.
Create your own surveyChecking submission availability…
This is a demo. We count starts and submissions only. Your answers stay in your browser and are never sent or saved.
Activity · no starts yet
How to Adapt the Questionnaire
Replace the escalation note with the verified, monitored route your organization actually uses. State who receives reports, the real monitoring hours, and a fallback if the usual account or device is affected. Keep no-upload instructions prominent. The form must not invite passwords or technical evidence dumps. Tell reporters that 'not sure' is acceptable, and obtain security-team review before using a survey platform for real incident notifications.
When to Ask
Make the approved route easy to find before an incident occurs. Encourage prompt use according to the organization's process, without asking people to investigate first. A public template demo is only a demonstration and does not notify a security team.
How to Use the Responses
Treat each response as an unverified report. The authorized team should review observation time, affected service, observed behavior and actions already taken together, then use the established incident process. Do not auto-label an employee careless, infer the scale of a breach from one report, or treat a submission counter as incident prevalence. Keep case status, technical evidence and response actions in the approved incident-management system. Document how follow-up will occur when contact information is missing.
What the Research Adds
Burda, Allodi, Serebrenik, and Zannone's 2024 university case study interviewed 49 employees who had reported phishing emails and identified “13 main themes driving reporting motivations.” It highlights reporting as a human process to understand, rather than assuming a policy guarantees participation. Its reporter-only sample does not validate this form or prove it increases reporting. The study covers phishing, not every incident type listed here. Read the phishing reporting study .
Frequently asked questions
Does this establish that a breach happened?
No. The form records an observation for qualified review. A suspicious event and a confirmed breach are different conclusions.
Should someone attach the suspicious file?
Not through this template. Use the security team's separately approved evidence-transfer process if requested; the initial form deliberately excludes files and sensitive contents.
Is the public demo an incident reporting service?
No. Demo answers stay in browser memory and are not sent to a security team. Organizations must establish and test their own reporting process before real use.
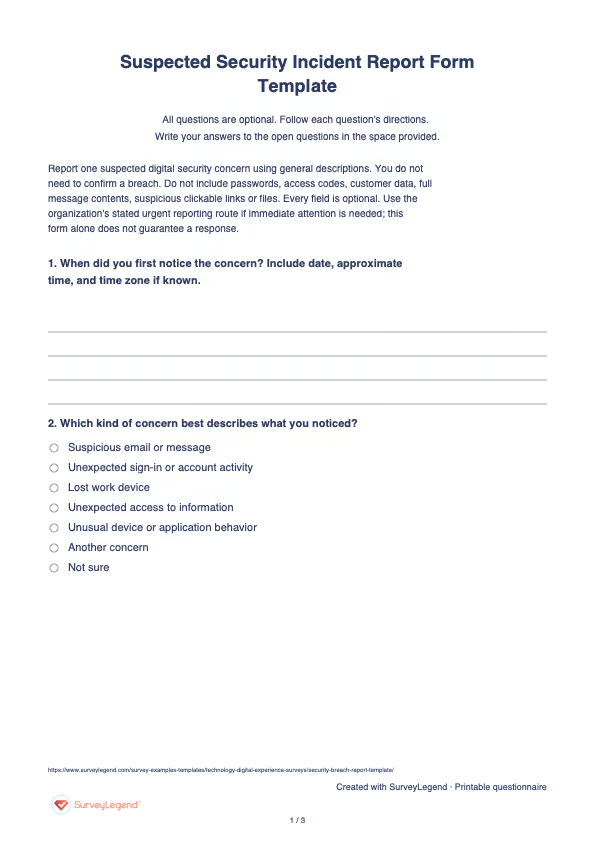
Printable Suspected Security Incident Report Form
Provide all seven fields with ample space for a brief non-sensitive observation. Print the approved urgent route and no-secrets/no-files instruction at the top. Store and deliver completed paper forms only through the security team's approved process. Paper responses need separate review or manual entry; they are not automatically added to online results.
 Download the questionnaire
AI Prompt: Suspected Security Incident Report Form
Copy this suspected security incident report form prompt into an AI assistant to prepare the questionnaire. Review the result, then build and customize it in SurveyLegend. It does not automatically create or transfer a survey.
Suspected Security Incident Report Form Prompt
Copy the prompt into an AI assistant to draft the questions, then build your survey in SurveyLegend.
Sign in to SurveyLegend to build your suspected security incident report form
-
 Website Feedback Survey Template This website feedback survey template helps you learn why visitors came to your website, whether they completed their task, and what got in the way. Its six questions cover the visit’s purpose, outcome, and difficulties. Adapt the questions to your website and create your survey with SurveyLegend.
-
 AI Readiness Assessment Template Use this AI readiness assessment template to identify what your team still needs before starting an AI pilot. Nine questions cover the proposed task, data access, review responsibilities, support, and success criteria. Build the assessment in SurveyLegend to bring practical questions into one conversation before choosing the next step.
-
 App Feedback Survey Template A broad app rating rarely tells a product team where to start. Anchor feedback to a recent session and ask what the user was trying to do. Keep bug investigation separate from the feedback form so people are not asked to submit sensitive screenshots or account data.
-
 SaaS Onboarding Survey Template Creating an account is only one part of onboarding. Ask whether users attempted their intended task and what happened next. Include people who did not get started so you do not hear only from successful users.
-
 Software Evaluation Survey Template A software demo can look convincing without showing whether the tool fits your work. Give evaluators the same trial task and ask what they could complete. Keep their experience separate from technical checks that require specialist review.
-
 Blockchain Pilot Survey Template This blockchain pilot survey helps participating teams describe what must be agreed before a trial begins. It starts with the business task, not a promise that blockchain will solve it. Build the original questionnaire in SurveyLegend and use the responses to prepare a focused scoping discussion.
-
 CRM Software Survey Template A CRM can hold plenty of information and still make routine work harder than it needs to be. Ask users where the process breaks down before deciding whether the answer is training, clearer ownership, better data, or a system change. This SurveyLegend questionnaire keeps those possibilities separate.
-
 Employee Cybersecurity Awareness Survey Template A completed training module does not tell a security team whether the reporting route is clear. SurveyLegend helps gather practical feedback from employees without asking anyone to paste a suspicious link or reveal a password.
-
 General Internet Usage Survey Template Being online does not necessarily mean someone can complete every task they need to do. This SurveyLegend questionnaire separates access, use, and requested support so those different needs remain visible.
-
 Help Desk Ticket Form Template “It does not work” leaves a support team with several questions. Which tool was involved? What was the person trying to do? What appeared instead? SurveyLegend helps you collect those details in a consistent form before the help desk reviews the issue. Use your established support route to associate the report with a requester.
-
 Home Security Survey Template Use the questionnaire before choosing a community workshop or resident information pack. Renters and owners may have different decision roles, so a single list of recommended purchases may miss what people need. SurveyLegend's example focuses on useful information and practical barriers, not on identifying weaknesses in individual homes.
-
 Internet of Things Survey Template A smart light and a connected lock serve different needs. Name one device or concept, describe what it does in plain language, and invite people who have not used it as well as current users. This survey explores usability and information needs; it does not test device security.
-
 Internet Speed Experience Survey Template A connection can feel slow during one activity and work well for another. Asking only whether someone is satisfied leaves that difference unexplained. SurveyLegend's questionnaire helps you collect a focused account of recent experience; it does not run a speed test or measure download and upload rates.
-
 Internet Speed Feedback Survey Form Ask adult campus Wi‑Fi users about the past seven days and name the exact network in the invitation. A 2024 IPB University thesis measured throughput, delay, jitter and packet loss across campus locations and tasks, then separately surveyed 50 students. Its abstract reports “a survey of 50 students rated connection speed at 3.04 (fair).” Read the university thesis abstract. That distinction matters: a person's rating and a network instrument's Mbps, delay or packet loss are different evidence. The IPB results describe one campus and do not validate this original SurveyLegend form.
-
 Mobile Phone Replacement Survey Template Invite adults who replaced their main phone within the past 12 months and ask about that one decision. Replacing a phone because it stopped working is different from choosing a new feature while the old phone still works. SurveyLegend's example keeps those reasons separate so researchers can identify useful follow-up questions.
-
 Online Professional Networking Survey Template A large contact list does not tell you whether someone found useful advice or a meaningful conversation. This SurveyLegend questionnaire focuses on what people are trying to achieve and the interactions they actually describe.
-
 Phone Survey Participation Template This phone survey participation template helps a research team improve how it invites adults to one planned telephone study. Show a plain-language invitation first, then ask what would make participation practical. SurveyLegend can be used to build the feedback questionnaire; the team must manage recruitment and calls through its own approved process.
-
 Security Awareness Survey Template Knowing where guidance is located, feeling confident about reporting, and following a procedure are different things. Ask about each carefully rather than treating confidence as proof of security knowledge.
-
 Smart Home Survey Template A device can work reliably while leaving people unsure how to change its settings or understand its data collection. Ask about those experiences separately rather than combining them in one satisfaction rating.
-
 Software Satisfaction Survey Template Use this software satisfaction survey template with people who have used one established product during the past four weeks. The seven optional questions separate overall satisfaction, task ease, reliability, information quality, support, and one improvement. Browse related technology templates, then adapt this focused version in SurveyLegend.
Free survey maker
Start creating surveys today for free
Create and bring your ideas to life with the survey tool used by people all over the world.
Ready to collect better research data?
Create academic surveys and questionnaires from ready-made templates.